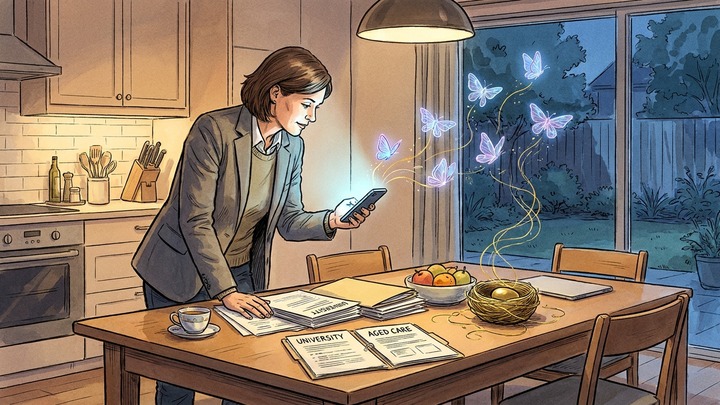
When a mobile phone vibrates flashing a six-digit verification code apparently sent by a major superannuation fund, the temptation to tap approve and return to what you are doing is almost automatic.
That domestic intersection of high net worth and mental fatigue has become the primary stage for a new type of financial crime. While global headlines at the end of October 2026 focused on billions of dollars vanishing in the largest cryptocurrency exchange hack in history, cybersecurity analysts have been tracking a far more personal threat. Transnational syndicates, armed with generative artificial intelligence, have turned their attention to the $4 trillion sitting in Australian and New Zealand Superannuation accounts.
Recent intelligence from the Australian Signals Directorate and New Zealand's National Cyber Security Centre points to a sharp rise in a technique known as identity synthesis. In the wake of massive data breaches at telecommunications firms, health insurers, and financial services providers, millions of identity records circulate permanently on dark web markets. A driver's licence number, a Medicare card, and a passport scan used to be enough to pass a standard hundred-point identity check. Now, autonomous AI agents harvest those leaked fragments and combine them with public professional footprints.
Modern retirement heists rarely involve a breach of a fund's core ledger. Instead, criminals use automated scripts to hijack a member's online portal via credential stuffing and SIM-swapping. Once inside, they exploit the very machinery built to make the system efficient. Protocols like the Australian Taxation Office's SuperMatch and electronic rollover rails were designed to help workers consolidate multiple accounts in days rather than weeks. In the hands of an automated syndicate, those high-speed rails allow an entire life's savings to be quietly rolled over into a newly fabricated self-managed super fund or a cryptocurrency-linked platform before the true owner notices a lost mobile signal.
Even biometric defences are buckling. Interactive voice response systems, once marketed by major banks and trustees as an unbreakable seal, can now be fooled by voice-cloning algorithms that require just three seconds of audio scraped from a public webinar, a company video, or a standard voicemail greeting. In New Zealand, where KiwiSaver funds remain largely locked until age sixty-five, the Financial Markets Authority has tracked a surge in deepfake investment endorsements targeting savers approaching the sixty-to-sixty-five transition window, alongside falsified financial hardship applications drafted by large language models.
The toll of watching thirty years of deferred wages evaporate can upend a household. Resolving a compromised retirement account or freezing a fraudulent rollover frequently takes months of forensic accounting, ruining sleep and physical health. Unsurprisingly, the 2026 PwC Voice of the Consumer Survey found that digital trust and cybersecurity anxiety now sit right alongside everyday health and cost-of-living pressures as primary concerns for middle-aged households.
Who should bear the cost of this has sparked a ideological divide.
On the left, consumer advocates, trade unions, and progressive policymakers argue that multi-billion-dollar superannuation trustees and retail banks have been negligent. For decades, institutions have collected billions in compulsory administration and investment fees while relying on outdated SMS one-time passwords and fragile third-party administrators. Because retirement contributions are mandated by law in Australia, progressive analysts contend that the state and its licensed trustees hold a non-delegable duty to guarantee the cryptographic safety of those funds. They point to the United Kingdom's mandatory reimbursement rules for authorised push payment fraud as a necessary model, arguing that banks, telecommunications providers, and super funds should automatically compensate defrauded savers unless gross negligence is proven.
On the right, free-market economists and industry groups counter that blanket statutory reimbursement creates severe moral risk. If institutions are forced to underwrite every compromised personal email password or careless click, the massive compliance and insurance costs will simply be passed straight back to everyday savers through higher administrative fees and lower net returns. Conservative commentators emphasise personal digital custody, arguing that high-income professionals must apply the same vigilance to their digital portals as they do to the deadbolts on their front doors. They also warn that heavy-handed bureaucratic friction, such as multi-week freezes on legitimate rollovers, penalises agile investors and stifles competition between legacy industry funds and self-managed platforms.
Between these two sides, regulators are attempting to tighten the screws. The Australian Prudential Regulation Authority has stepped up enforcement of Prudential Standard CPS 234, demanding that trustees maintain information security capabilities that match the speed of modern threats. Yet regulatory standards move slowly, and machine-driven syndicates adapt by the hour.
Bridging the gap requires both institutional reform and immediate personal action. Technologists and policy innovators are calling for two structural changes across the retirement sector. The first is the mandatory replacement of SMS verification codes with FIDO2-compliant hardware security keys or cryptographic passkeys for any balance rollover or withdrawal exceeding $10,000. The second is the introduction of a compulsory cooling-off vault: a seventy-two-hour time-locked delay triggered whenever a member requests a transfer to a newly established self-managed fund or an unfamiliar bank account, accompanied by multi-channel verification.
Until trustees build those circuit breakers into the plumbing of the system, middle-aged savers have to act as their own security guards. A practical defence takes little effort and relies on four straightforward habits.
First, decouple your retirement accounts from your everyday digital life by creating a dedicated, unpublicised email address used solely for superannuation, banking, and government portals like myGov or RealMe.
Second, strip SMS two-factor authentication from every financial login and replace it with a app-based authenticator, while setting a strict corporate PIN with your mobile carrier to block unauthorised SIM swaps.
Third, audit your linked government services to ensure SuperMatch or automatic rollover functions cannot be triggered without secondary notification, and ask your fund whether you can place a voluntary administrative freeze on outbound transfers.
Fourth, delete public voice samples from professional networking sites and replace personal recorded voicemail greetings with the default automated carrier voice.
Compounding interest only works if the principal remains in the vault. Treating a retirement balance like an active treasury rather than a forgotten savings account is the new price of peace of mind.